
Central Bank mandate forces lenders toward biometric confirmation to curb SIM-swap fraud and phishing attacks
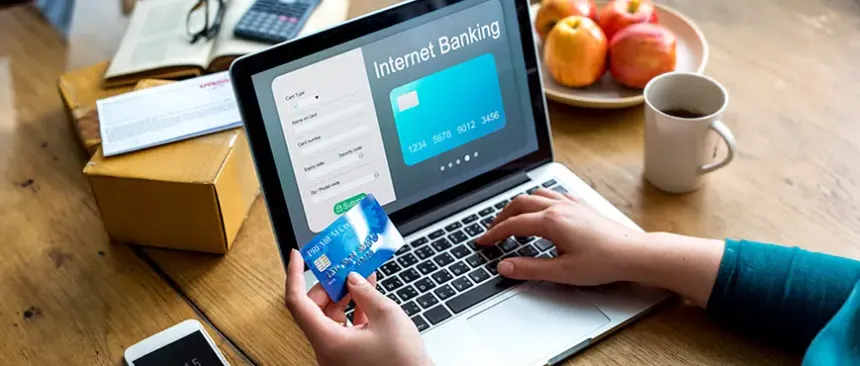
DUBAI, Sept. 17, 2026 : Banks across the United Arab Emirates are dismantling traditional SMS and email one-time passwords for online card payments, replacing them with encrypted in-app authorizations and biometric verification.
Shoppers completing digital checkout in the UAE will notice an immediate difference at the payment gateway. Instead of waiting for a six-digit code via text message, transactions now trigger instant notifications prompting users to authorize the charge directly inside their bank’s mobile application.
The industry-wide transition follows direct regulatory intervention by the Central Bank of the United Arab Emirates (CBUAE). Under regulatory guidelines issued to licensed financial institutions, traditional text and email delivery methods for online transaction approval are being phased out in favor of secure, device-bound protocols. The regulator set a final compliance deadline of March 31, 2026, prompting lenders to roll out app-centric verification frameworks across retail accounts.
During an online purchase, entering card details no longer brings up a code entry field. Consumers receive a prompt on the merchant screen to review the pending order on their registered smartphone. Some lenders dispatch a companion text alert advising the cardholder that an authorization request is pending.
Customers then open their banking app, navigate to pending approvals or tap a push prompt, and inspect the merchant name, charge amount, and currency. Authorization requires passing a biometric check—typically facial recognition or fingerprint scanning—or entering a bank-specific digital PIN such as a Smart Pass code. Transactions typically carry a short countdown window, expiring automatically if ignored.
The push away from SMS stems from long-standing structural vulnerabilities in telecommunications channels. Fraud syndicates operating across the region have increasingly deployed SIM-swap schemes, convincing mobile carriers to reassign victim phone numbers to attacker-controlled SIM cards. Combined with sophisticated social-engineering calls and phishing websites designed to capture six-digit codes in real time, SMS-based verification had evolved into a primary target for financial crime.
Because in-app approvals occur within an encrypted software ecosystem tied to a registered hardware device, intercepted telecommunication data cannot validate a charge. Without the authenticated smartphone and registered biometric data, unauthorized parties cannot complete online transactions.
Implementation details vary across institutions. Major lenders, including Dubai Islamic Bank, Emirates NBD, and First Abu Dhabi Bank, have transitioned card authentication pathways through iterative mobile updates, with some maintaining transitional options while customers register their biometric credentials. Financial institutions are urging cardholders who have not activated mobile banking apps or biometric permissions to complete setup promptly to avoid payment disruptions.